FireSale HackBoy

Knowledge Shared By FireSale HackBoy...

Hacking

The Art Of Exploitation...

Ethical Hacking

Security Experts...Same Techniques To Make Hacker's Stuff Useless.

Black Hat Hacking

Dark Side Of Hacking... In Short Destruction Of Cyber Stuff.

Digital Stuff

All The Digital Stuff Is Under The Influence Of Cyber Attacks... Be Safe

Wednesday, October 2, 2019

A pervert Yahoo employee hacked 6,000 accounts using internal system

By Waqas

A former Yahoo engineer hacked 6,000 Yahoo Mail account to extract the personal information of victims primarily sexual images and videos.

This is a post from HackRead.com Read the original post: A pervert Yahoo employee hacked 6,000 accounts using internal system


October 02, 2019 at 04:23PM

Tuesday, October 1, 2019

World Economic Forum names Cyber Attack as the top risk for the US, Canada, and Europe

According to a survey conducted and published by the World Economic Forum (WEF), cyber-attacks are named as leading risks for business executives hailing from companies operating in Canada, the United States and Europe.

The study which was conducted in the association with Zurich Insurance Group and Marsh & McLennan Cos identified the top 5 risks which are creating a shutdown crisis for companies on a global scale.

WEF survey titled “Regional Risks for doing business in 2019,” says Unemployment, underemployment, energy price jolts, and fiscal crisis came into the listing of major threats to companies after cyber attacks. Astonishingly data fraud or theft which is related to Information Security stood tall in the list of top ten risks along with infrastructure failure.

Regionally, the top five risks in the United States are as follows- 1.) Cyber Attacks 2.) Data Frauds, 3.) Terrorist attacks, 4.) Critical information infrastructure breakdown and 5.) Failure of critical infrastructure

Coming to Canada the top 5 reported risks are 1.) Cyber Attacks, 2.) Data Fraud, 3.) Extreme weather events 4.) Energy Price Shock 5.) Failure of Regional and global governance

For Europe 1.) Cyber Attacks 2.) Asset Bubble 3.) Interstate conflict 4.) Energy Price Stock 5.) Fiscal Crisis stood as the top 5 risks.

Note- The risks lined up in the survey report titled “ Regional Risks for Doing Business 2019” are based on the 12,897 responses from executives in 133 economies and the survey was reportedly carried out from January to April 2019.

The post World Economic Forum names Cyber Attack as the top risk for the US, Canada, and Europe appeared first on Cybersecurity Insiders.


October 02, 2019 at 09:50AM

Ransomware attack on 621 hospitals, 500 schools and 169 businesses in the United States

A recent survey made to find the number of affected victims with ransomware in the United States has found that over 621 hospitals, 500 schools, and 169 businesses were hit by the said malware in 2019 alone.

Cybersecurity firm Emsisoft issued a report yesterday stating the above stats and added that the estimate of financial loss in Albany and New York alone might stand at $300,000- only to restore data following a ransomware attack.

Another security firm named Armor has said that over 15 US school districts accounting to over 100 schools were hit in the past two weeks alone and the list of school districts is as follows- Northshore School District, Smyth County Public Schools, Guthrie Public School, Houston County Board of Education, Mobile County School District, Wyoming Area School District, Jackson County School District, Wakulla County School District, Souderton Area School District, Rockford Public Schools, Mad River Local Schools, Papillion La Vista Comm Schools, Wallenpaupack Area School District and Ava R-I School District.

Armor states that most of the ransomware incidents were caused by Ryuk ransomware and some other active malware strains.

Unfortunately, both the firms which are into cybersecurity did not confirm the amount which went into the ransom payments to hackers as the heads of the impacted school districts weren’t ready for the disclosure.

Note- On the contrary, as per the report released by the K-12 Cybersecurity Resource Center, out of 128 cybersecurity incidents on US K-12 Schools experienced in 2019, only 23 attributed to ransomware.

The post Ransomware attack on 621 hospitals, 500 schools and 169 businesses in the United States appeared first on Cybersecurity Insiders.


October 02, 2019 at 09:48AM

The MITRE ATT&CK Model: A More Effective Way to Detect and Block Cyber Attacks

There have been a variety of models used to define different attack methodologies. Perhaps the most common is Lockheed Martin’s Cyber Kill Chain, that identifies the individual phases of malware attacks. Defining the phases enables you to better understand how to anticipate, prevent, detect, and respond.

Lockheed derived the name from the military term “kill chain” used to define the traditional attack phases from the identification to the destruction of a target. The guiding principle is that when you understand how an adversary operates, you can determine the best opportunity to stop the attack before it’s launched. 

Similarly, the Cyber Kill Chain focuses on malware based attacks. Althoughthe Cyber Kill Chain of an individual attack can be generalized to describe other cyber attacks, sharing that information is difficult. Enter MITRE ATT&CK.

A New Approach

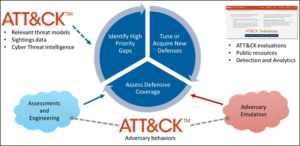
MITRE ATT&CK intends to be a knowledge base of adversary tactics and techniques. Its organization of tactics and techniques provides a framework for threat models and techniques. This is a much more comprehensive approach to identifying and thwarting cyber attacks than focusing only on the malware. It also recognizes the fact that attackers may not follow every phase of the defined methodology. 

Attackers might not be as organized as you believe. At the same time, some attacks might not require technology, and therefore do not have to go through all of the phases of a traditional attack. For example, an insider might already have access to internal information and only needs to walk out of the door with it.

Source: Andy Applebaum, MITRE ATT&CK™

There are a variety of uses for this knowledge base, including identifying and prioritizing security countermeasures, analyzing attacks in progress, and performing red teaming.

For example, if you are in the healthcare space you can see which threat actors are targeting your industry  and the techniques and tools they tend to leverage. This will allow your blue team to practice threat hunting aimed at detecting those TTPs, and ensure you prioritize your security investments appropriately. 

An Attack Hits – What’s Next?

When you detect an attack, the first step is to use the model to help you determine all possible points where you may have been compromised, and analyze the extent of the damage. 

For example, if you detect malware on your systems, you would investigate how the malware might have got on the systems, and search for other possible compromises. Or if you detect spyware, you can more easily determine how the data is being exfiltrated. This will enable you to stop future attacks, or if you caught the attack in time, prevent data exposure or theft altogether.

At the same time, MITRE ATT&CK can serve as a red team playbook. It allows penetration testers to create realistic attack scenarios and provides technical guidance on how to implement them. 

The ATT&CK knowledge base is so information-rich that it behooves any security professional to at least become familiar with it at a high level. We all have different levels of involvement with cyber attacks, and we should be proactive in knowing where to access relevant information before and attack hits. 

The post The MITRE ATT&CK Model: A More Effective Way to Detect and Block Cyber Attacks appeared first on Cybersecurity Insiders.


October 02, 2019 at 02:22AM

VMware Acquisitions Highlight the Importance of DevSecOps

Cloud-security_picIn the digital age, security can no longer be an afterthought. As organizations modernize their IT environments through digital transformation initiatives, it’s become more critical than ever to bake security into new applications from the start.

Virtualization giant VMware recognizes this new reality, which explains why it has decided to acquire two companies that give the company a stronger foothold in digital transformation and cybersecurity.

One of the companies, Pivotal Software, brings to VMware a platform for developing applications in the cloud. The other, Carbon Black, has a cloud-native endpoint protection platform that ensures this is done securely. Together, the acquisitions send a strong signal by VMware and its parent company, Dell EMC, that it is serious about the role DevSecOps plays in developing modern, cloud-based workloads.

VMware CEO Pat Gelsinger said the acquisitions address two critical priorities for VMware – “building modern, enterprise-grade applications and protecting enterprise workloads and clients. With these actions we meaningfully accelerate our subscription and SaaS offerings and expand our ability to enable our customers’ digital transformation.”

From a security perspective, the move is especially significant. While in the past, security often took a backseat in development, it has become a priority. As organizations build workloads in the cloud and integrate them into hybrid environments, they are thinking about security from day one.

“We now have the opportunity to seamlessly integrate Carbon Black’s cloud-native endpoint protection platform into all of VMware’s control points. This type of bold move is exactly what the IT and security industries have been looking to see for a very long time,” said Patrick Morley, CEO, Carbon Black.

Addressing the Skills Gap

In highlighting the importance of DevSecOps, the VMware acquisition of Carbon Black also helps call attention to the need for advanced cybersecurity and cloud security skills. Currently, there is a shortage of nearly 3 million cybersecurity workers worldwide, something (ISC)² is helping to address with its cybersecurity education curriculum.

Part of (ISC)²’s Professional Development Institute (PDI), DevSecOps: Integrating Security into DevOps is a self-paced online course that delivers in-depth instruction on making security an integral part of the development cycle to achieve DevSecOps. The course is targeted at experienced cyber, information, software and infrastructure security professionals looking to launch or strengthen a DevSecOps program in their organizations – or make security an integral component in their digital transformation strategies.

(ISC)² also recently launched a course on Cloud Basics as part of PDI, which is the first in a series of courses on the cloud, designed to provide a solid understanding of cloud computing including key drivers and rationale for moving to the cloud, cloud architecture and computing concepts and characteristics, cloud service and deployment models, and cloud brokers.

The growing popularity of (ISC)²’s Certified Cloud Security Professional (CCSP) certification has been well-documented. In January 2019, Certification Magazine recognized it, for the fourth year in a row, as the “Next Big Thing” in its annual salary survey. The magazine’s survey respondents reported that the CCSP would be the most-pursued certification by security professionals in 2019, just ahead of the CISSP certification. (ISC)² research in 2018 showed a similar trend, with the CCSP and CISSP cited as the most sought-after security industry certifications globally last year.

As the VMware acquisitions demonstrate, as cloud computing applications and security continue to intersect, it will drive a greater need for more education among cybersecurity professionals to ensure that DevSecOps is a foundational aspect of the cloud migration process.

The post VMware Acquisitions Highlight the Importance of DevSecOps appeared first on Cybersecurity Insiders.


October 01, 2019 at 09:08PM

Ransomware attack leads to shutting down of California based healthcare service provider

Can you believe that a ransomware attack on a healthcare provider has forced it to shut down its services by this year-end..? If not, here’s a news share that will enlighten your minds on the potential of a malware attack which has led to the closure of California based Wood Ranch Medical(WRM) services provider.

Going into the details, in August this year servers containing digital health records of patients related to Wood Ranch Medical were hit by ransomware. As a result of which data was encrypted including the data on the backup servers.

As the data recovery was not the possible rebuilding of medical records became a hard task for the IT staff of healthcare.

Since the hospital is not in a position to continue with the operations, it has made it official that it will close its practice and medical care operations from December 17th,2019. The said medical practitioner will then find another medical service provider to its on-account patients. All the WRM patients will be mailed the details of the ransomware incident and what to do next to protect or monitor their personal information.

Readers of Cybersecurity Insiders should note down a fact over here that WRM happens to be the second healthcare service provider to shut down its services in this year- as Michigan based Brookside ENT and Hearing Center stands first as hackers managed to wipe out the entire database of the service provider as the hospital staff failed to pay a demanded ransom of $7000 in BTC on time.

In the meantime, the US Senate has done a federal ramp up last week by endorsing the Cyber Hunt and Incident Response Teams Act drafted by the Department of Homeland Security (DHS).

The objective of the newly established Ransomware law will be to advise organizations on how to take protective measures against the prevailing cyber threats and how to deal with the situation if in case they get victimized by chance.

In shorty, the US Senate has passed a ransomware law that will provide public and private organizations legislative protection against cyber attacks and this includes cyber incidents hitting police departments, schools, educational institutions, hospitals, banks, and other businesses.

The post Ransomware attack leads to shutting down of California based healthcare service provider appeared first on Cybersecurity Insiders.


October 01, 2019 at 08:49PM

Leaky database exposes tax records of 20 million Russians

By Sudais

According to a report by Comparitech, more than 20 million tax records were found on an unprotected Amazon Web Services (AWS) Elasticsearch Cluste

This is a post from HackRead.com Read the original post: Leaky database exposes tax records of 20 million Russians


October 01, 2019 at 08:45PM